 ไทย
 English
Today, Security Operations Centers (SOCs) must handle continuously increasing volumes of security data from Cloud, Identity, Endpoint, API, and Behavioral Telemetry, while cyber threats are becoming increasingly sophisticated and may no longer appear in patterns that can be detected through Signatures or traditional rules alone.
The challenge is therefore not limited to threat detection, but also includes correlating data from multiple sources, understanding the context of events, prioritizing risks, and helping Security Analysts perform Investigation and Response more effectively.
Table of Contents
Frost & Sullivan observes that the industry is shifting from Security Operations that rely on Tools, Rules, and Manual Review toward a model in which AI supports Operational Judgment. AI is increasingly being used to interpret data, prioritize risks, and help Security teams manage growing volumes of information at Enterprise Scale.
One of the providers advancing this approach is Securonix.
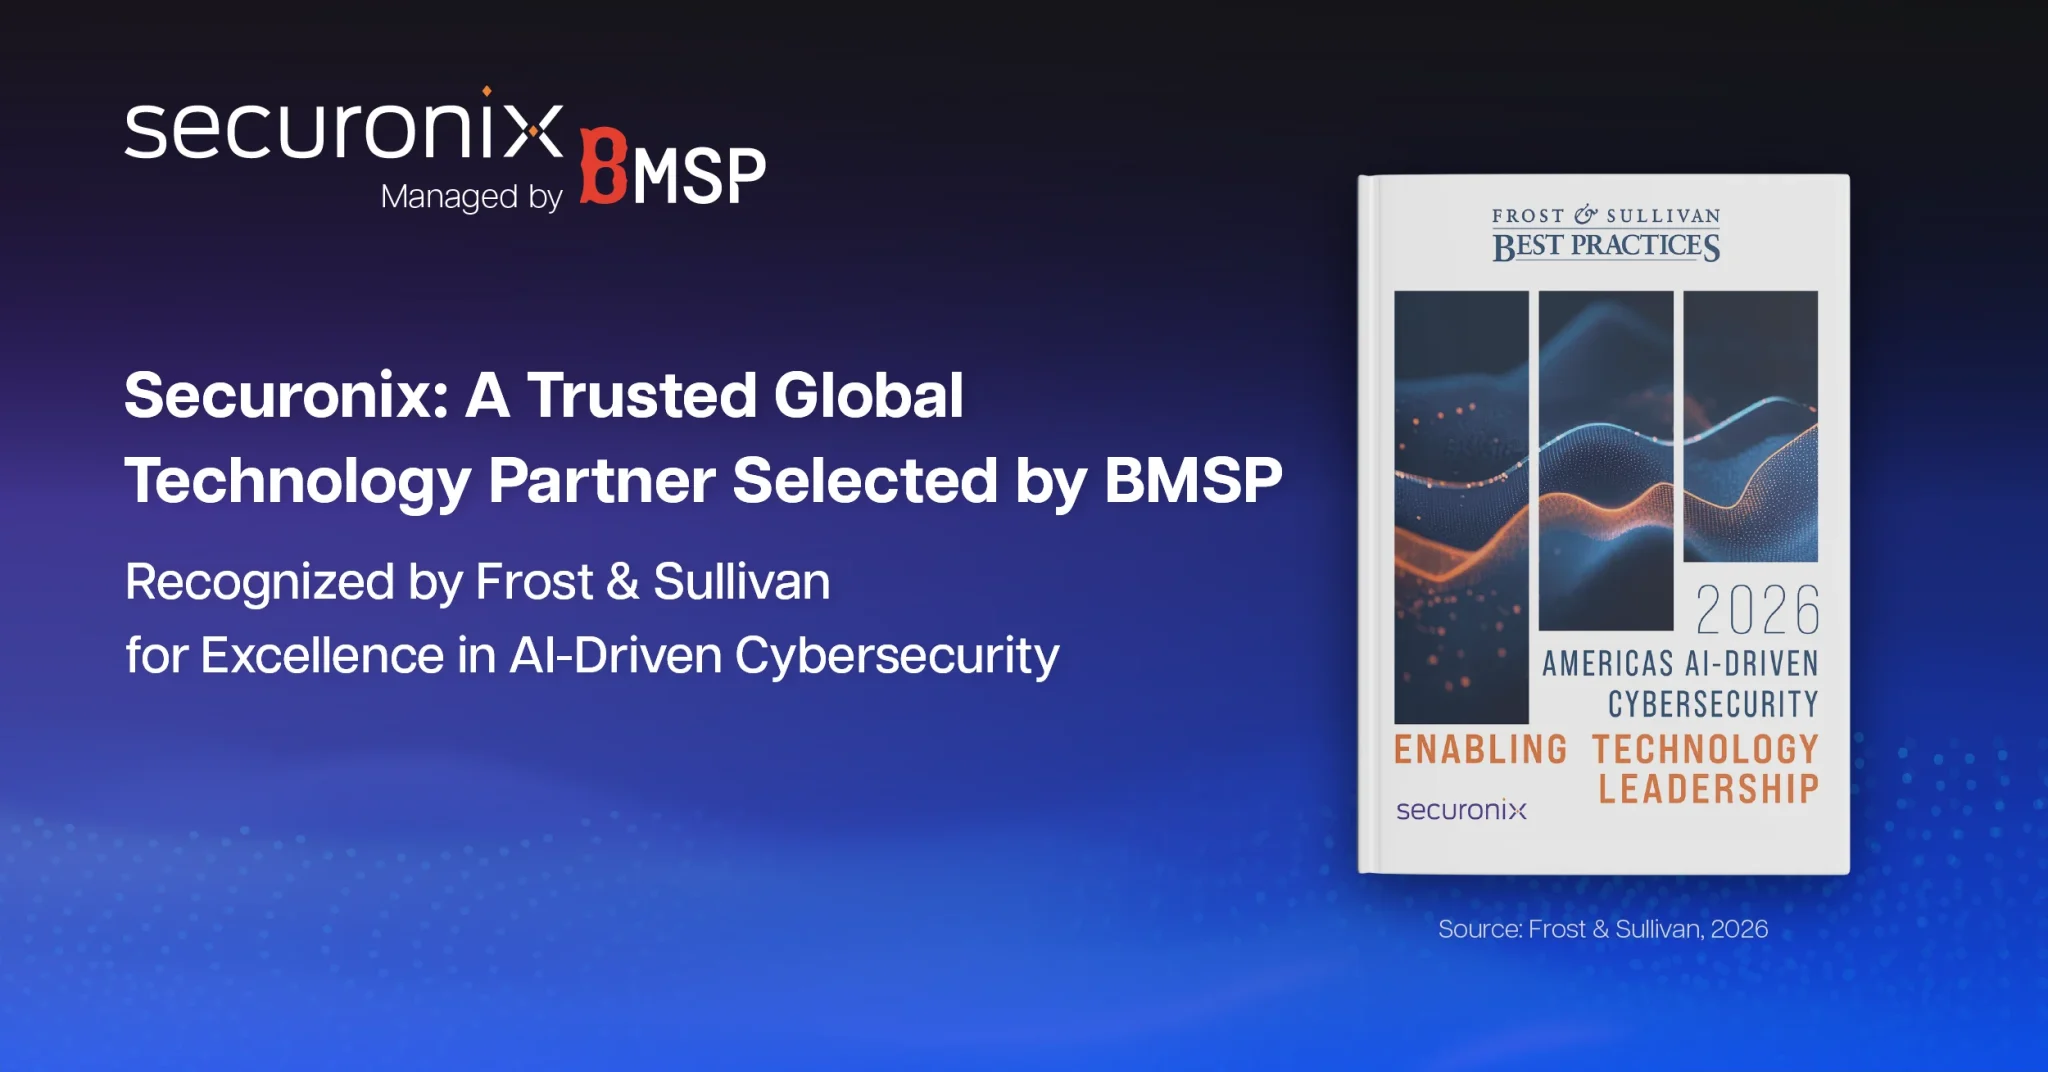
Most recently, Securonix received the 2026 Americas Enabling Technology Leadership Recognition in AI-driven Cybersecurity from Frost & Sullivan. The recognition highlights Securonix’s approach to integrating AI-assisted capabilities into Core SOC Workflows to improve Investigation, Alert Enrichment, Threat Prioritization, Insider Threat Analysis, and Analyst Decision Support.
Who is Frost & Sullivan?
Frost & Sullivan is a global research and consulting firm that analyzes markets, technologies, and industry trends, while evaluating and recognizing organizations that demonstrate excellence in innovation and customer value creation.
What does Frost & Sullivan see in Securonix?
According to Frost & Sullivan’s report, Securonix’s strength is not simply the use of AI as a Chatbot or Assistant, but the integration of AI directly into SOC workflows.
This approach helps organizations:
- Accelerate Investigation and Threat Prioritization
AI-assisted capabilities help Security teams analyze large volumes of data, correlate Security Signals, and prioritize Risks that require investigation more quickly. - Reduce repetitive work for Security Analysts
AI can assist with tasks such as Data Enrichment, Investigation Preparation, Cross-tool Correlation, and Threat Summarization, allowing Analysts to spend more time on work that requires analysis and decision-making. - Maintain Human Oversight and Enterprise Governance
Securonix does not focus on replacing Analysts with AI. Instead, it follows a Human-Machine Collaboration approach in which AI helps handle repetitive tasks while Analysts continue to provide oversight, apply Judgment, and make decisions on critical matters. - Manage Security Telemetry and costs more effectively
- As Telemetry volumes from Cloud, Identity, Endpoint, and Hybrid Infrastructure continue to increase, organizations need to balance Visibility with SIEM and Storage costs. Securonix uses Data Pipeline Manager (DPM) to Filter, Route, and Prioritize Telemetry based on Security Value, Compliance Requirements, and Operational Relevance.
- Support Enterprise-scale Security Operations
Using AI to reduce labor-intensive and time-consuming Analyst tasks helps improve team Productivity and Scalability without requiring Operational Overhead to increase at the same rate.
The key concept is to use AI to improve the efficiency of Security Operations processes, from data analysis and Investigation to threat prioritization.
Securonix and the Evolution of Security Operations

Securonix focuses on advancing Security Operations to handle increasing volumes of data and growing threat complexity by integrating AI-assisted capabilities into the actual Workflows used by Security Analysts.
According to Frost & Sullivan’s report, this approach covers Investigation, Alert Enrichment, Threat Prioritization, Insider Threat Analysis, and Analyst Decision Support, making AI part of the SOC’s Operational Workflow.
1. Helps reduce the burden of Alerts and repetitive tasks
Security Analysts spend a significant amount of time on repetitive tasks such as Data Enrichment, reviewing information across multiple Consoles, preparing information for Investigation, and creating Threat Summaries.
Securonix uses AI to help reduce these workloads, enabling Analysts to shift time away from Manual tasks and focus more on higher-value Investigation, Threat Analysis, and Response activities.
2. Improves Threat Investigation efficiency
Modern threats may not originate from a single Event with an obvious anomaly. Instead, they may emerge from multiple Weak Signals connected across time and behavior.
Frost & Sullivan states that Modern Security Operations need the ability to correlate Weak Signals, understand Context across Entities, and help Security teams identify Risk before an event develops into a clear Incident.
Securonix’s approach therefore focuses on using AI and Behavioral Analytics to support Analyst Investigation and decision-making, enabling faster analysis with greater context.
3. Increases SOC team Productivity
One of the areas Frost & Sullivan highlights about Securonix is the use of AI to address the Operational Efficiency challenges faced by SOC teams.
Rather than viewing AI solely as a Detection tool, Securonix focuses on reducing steps that create workload for Analysts, such as Alert Enrichment, Investigative Preparation, Multi-tool Correlation, and Executive-level Threat Summarization.
The intended result is to reduce the time spent on Routine work and increase the time Analysts can devote to tasks that require analysis and experience.
4. Manages Security Telemetry and costs
As organizations increasingly adopt Cloud, Identity, Endpoint, and Hybrid systems, the volume of Security Telemetry continues to grow. The challenge therefore involves not only Visibility, but also SIEM and Storage costs.
Securonix uses Data Pipeline Manager (DPM) to help Filter, Route, and Prioritize Telemetry based on Security Value, Compliance Requirements, and Operational Relevance. Valuable data for analysis can be retained at an appropriate level, while certain data can be managed through lower-cost Tiers.
This approach helps organizations expand Security Visibility while maintaining cost efficiency and greater predictability of expenses.
5. AI that remains under Human Oversight
Securonix follows an approach in which AI supports repetitive or time-consuming tasks, while Analysts continue to provide oversight, apply Judgment, and make decisions on critical matters.
Frost & Sullivan states that the future of the SOC is not focused on Fully Autonomous Operations, but on collaboration between humans and AI, with Governance and Human Oversight remaining essential components.
Why organizations should consider Securonix
For organizations looking to enhance Security Operations, selecting a Security Platform should not be based solely on threat detection capabilities. Organizations should also consider the efficiency of the overall operational process, from data management and detection to Investigation, prioritization, and Response.
Securonix takes an approach that integrates AI-assisted capabilities into Core SOC Workflows to:
- Increase the speed of Investigation and Threat Prioritization
- Reduce Manual work and Repetitive Tasks for Security Analysts
- Improve Analyst Productivity and Operational Efficiency
- Help manage Security Telemetry and control costs
- Support the expansion of Security Operations at Enterprise scale
- Apply AI under Human Oversight and Enterprise Governance
In addition, Securonix has also been recognized by Gartner in the SIEM market, having been positioned as a Leader in the 2025 Gartner Magic Quadrant for Security Information and Event Management (SIEM) for the sixth consecutive time. Gartner evaluates vendors based on key criteria including Ability to Execute and Completeness of Vision.
Previously, Securonix was also named a Customers’ Choice in the 2024 Gartner Peer Insights “Voice of the Customer” for SIEM, providing another perspective that reflects customer recognition alongside evaluations from industry analysts.
Recognition from both Frost & Sullivan and Gartner reflects Securonix’s position as a platform focused on advancing Security Operations across AI, data management, team efficiency, and Enterprise-scale deployment.
In addition, Securonix places importance on Data Governance and data security in Cloud environments, with investments in Sovereign AI Controls, Customer-level Data Isolation, and Cryptographic Separation to support Enterprise AI adoption.
Enhance Enterprise Security with Securonix Managed by BMSP
BMSP places importance on selecting high-quality Cybersecurity technologies that meet recognized standards and have gained international recognition to offer and deliver to our customers. We want customers to receive Best-in-Class Technology that can address real-world requirements and meet increasingly complex Cybersecurity challenges. BMSP therefore selected Securonix as a technology partner to deliver high-quality services to customers. This recognition of Securonix helps reinforce customer confidence that they will receive effective and high-quality services from BMSP.
For organizations that want to adopt Securonix to enhance Security Operations but require support from a team of experts, Securonix Managed by BMSP is a service that helps organizations use the capabilities of Securonix effectively. The BMSP team helps manage operations, reduce the workload of internal IT and Security teams, and enables organizations to focus more on responding to threats and critical business priorities.
Interested in Securonix Managed by BMSP? Contact BMSP to discuss and learn more about the service.